Air-gapped AI deployments are the backbone of how government agencies, defense contractors, and highly regulated enterprises run artificial intelligence (AI) without exposing classified or sensitive data to the open internet. As a result, the question for most program managers is no longer whether to isolate AI systems, but how to do it without stalling mission timelines. This guide walks through what air-gapped AI deployments involve, why they matter for DoD, Intelligence Community (IC), and Defense Industrial Base (DIB) teams, and how to plan an architecture that satisfies strict compliance frameworks.
Direct answer: Air-gapped AI deployments run AI models on infrastructure that is physically or logically disconnected from the public internet, so data never leaves an accredited boundary. This approach is standard for classified workloads that must meet IL5, CMMC, or SCIF requirements.
What Are Air-Gapped AI Deployments?
Air-gapped AI deployments are configurations where an organization's AI models, data, and inference infrastructure operate inside a network that has no direct path to the public internet. In practice, this means the AI never calls an external API, and no outbound connection can quietly leak information to a third-party model provider.
Specifically, an air-gapped setup differs from a typical "on-premises" installation. A server can sit inside a building and still connect to the internet for updates or model calls. Therefore, true isolation requires removing or tightly controlling that external link, often down to physical network segmentation enforced by hardware.
For defense and intelligence missions, this distinction matters enormously. A single misconfigured outbound connection can turn an otherwise secure system into a liability, which is why accreditation bodies scrutinize network boundaries so closely.
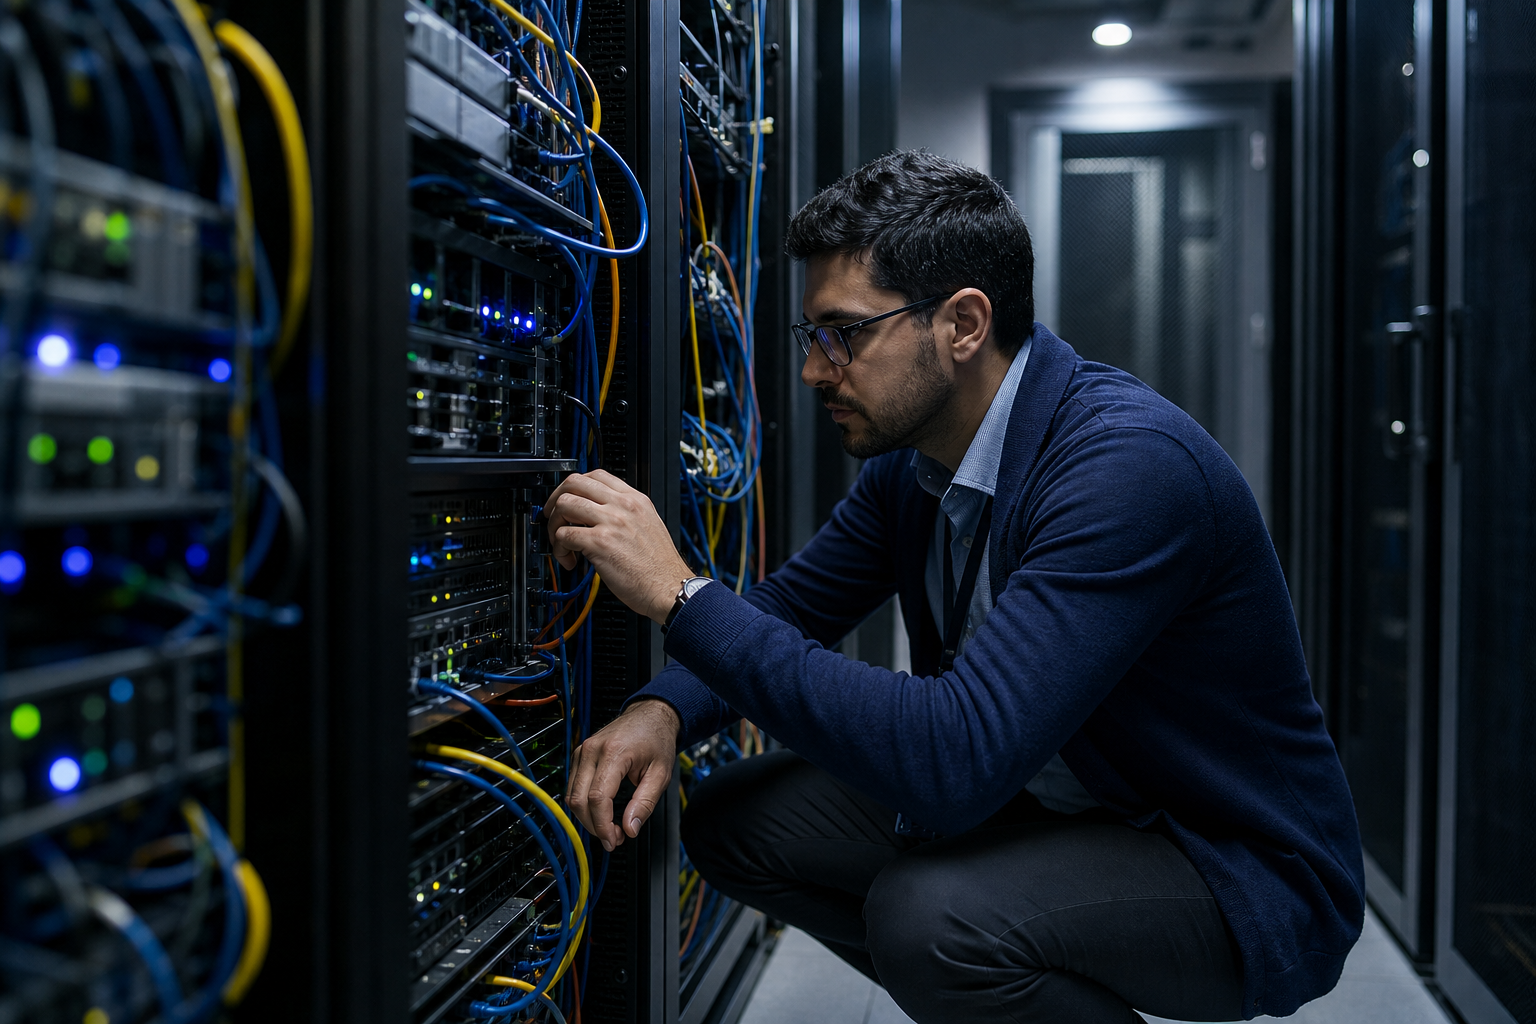
Isolated server infrastructure like this forms the physical foundation of air-gapped AI deployments.
Why Government and Defense Teams Need Isolated AI Systems
Government and defense organizations increasingly rely on isolated AI systems because the cost of a data exposure event in a classified program is measured in mission failure, not just dollars. Consequently, agencies cannot simply adopt commercial AI tools built for consumer convenience.
In particular, the Defense Industrial Base faces growing pressure from the Cybersecurity Maturity Model Certification (CMMC) program, which sets specific controls for handling Controlled Unclassified Information. Our related guide on CMMC-compliant AI software for defense contractors covers how these controls map directly to AI procurement decisions.
Furthermore, the Intelligence Community operates under even stricter boundaries, since many workloads require Impact Level 5 (IL5) authorization or full SCIF (Sensitive Compartmented Information Facility) isolation. As a NIST analysis of federal cloud security notes, control inheritance and boundary definition remain among the hardest parts of any authorization package, which is exactly where air-gapped AI deployments simplify the picture by keeping everything inside one clearly defined perimeter.
Above all, the goal is predictable risk. When an AI system cannot reach the outside world, entire categories of attack — including remote exfiltration and unauthorized model updates — simply do not apply. For a broader look at securing AI across sensitive sectors, see our guide on secure AI for government agencies.
Core Components of a Secure Air-Gapped AI Architecture
A well-built air-gapped AI architecture is more than a server with no internet cable. It requires layered controls that work together to protect data, verify identity, and detect misuse before it becomes a breach.
Post-Quantum Cryptography and CNSA 2.0
CNSA 2.0, the Commercial National Security Algorithm Suite, defines the cryptographic standards that National Security Systems must eventually adopt to resist both classical and future quantum computing attacks. According to the Wikipedia entry on post-quantum cryptography, quantum computers could eventually break widely used encryption like RSA, which is why forward-looking agencies are migrating now rather than waiting.
As a result, air-gapped AI deployments that encrypt data at rest and in transit using CNSA 2.0-aligned algorithms offer protection that extends well beyond today's threat landscape. This matters especially for data with a long classification shelf life.
CAC/PIV Authentication and DISA Alignment
Common Access Card (CAC) and Personal Identity Verification (PIV) credentials provide hardware-based multi-factor authentication before anyone can reach an isolated AI system. Because these cards are already standard across DoD and federal civilian agencies, integrating them avoids forcing users onto a separate identity system.
In addition, alignment with Defense Information Systems Agency (DISA) standards helps streamline the broader accreditation process. The DISA website outlines the security technical implementation guides that many air-gapped builds must follow, and meeting these benchmarks early reduces rework during formal review.
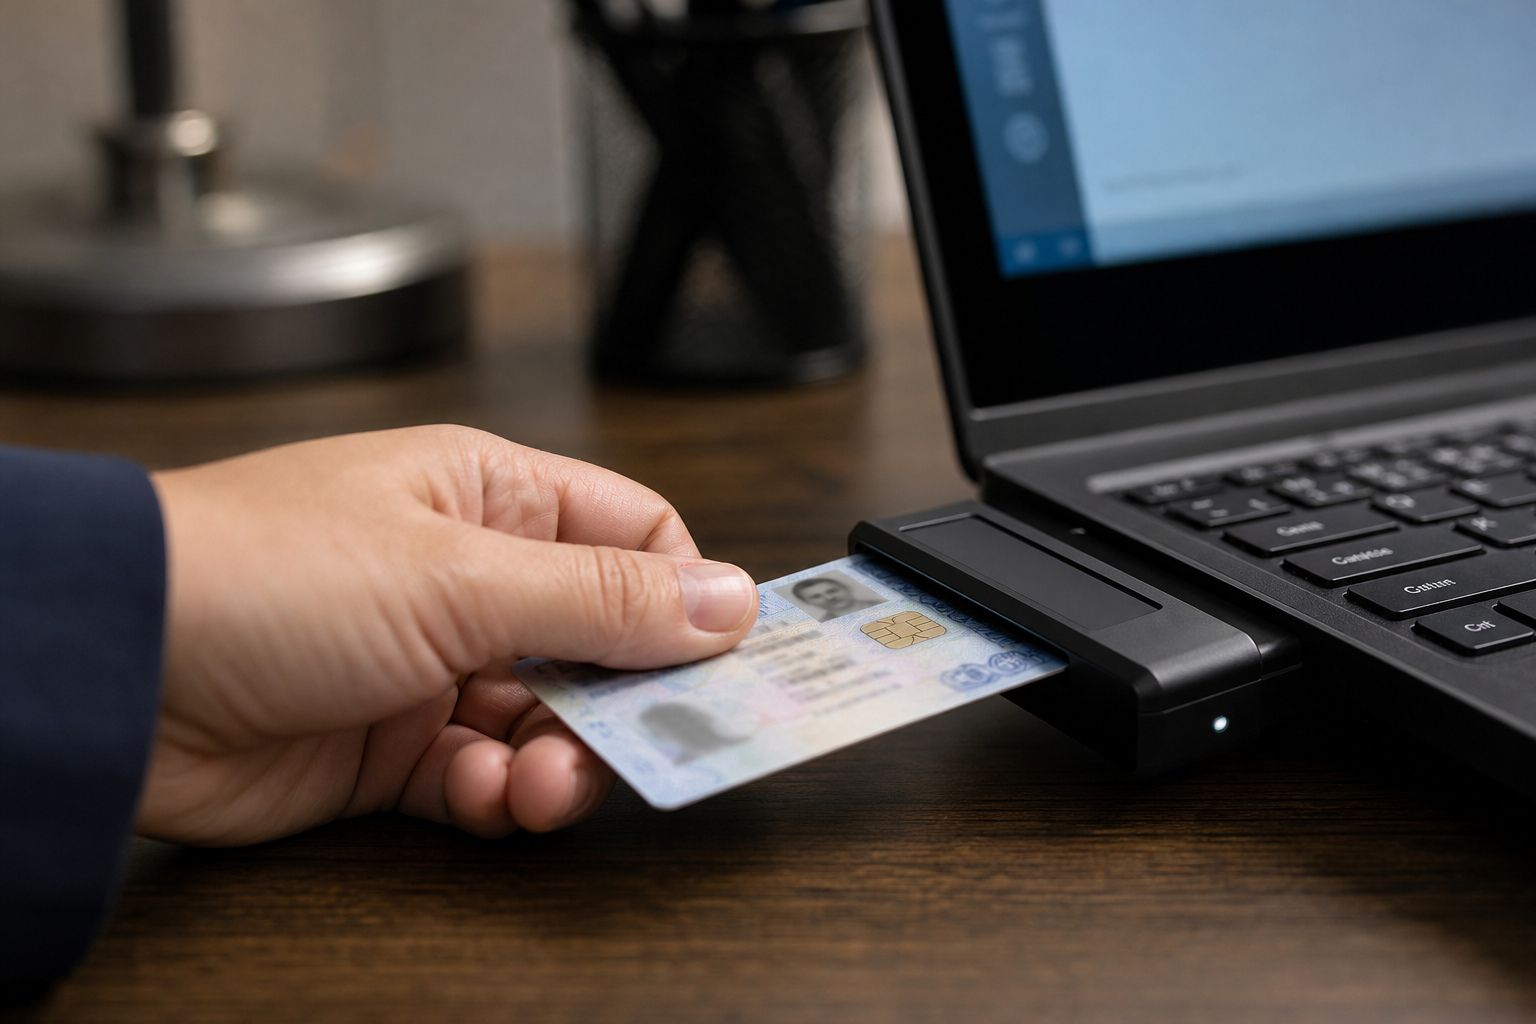
Hardware-based credentials add a critical identity layer to air-gapped AI deployments.
How to Deploy Air-Gapped AI Step by Step
Deploying an isolated AI environment follows a fairly consistent sequence, regardless of agency size. The following steps outline the typical path from planning to authorization.
- Define the classification boundary. Identify exactly which data, networks, and personnel fall inside the air-gapped boundary before selecting any hardware, since scope changes later cause expensive rework.
- Select IL5-ready infrastructure. Choose servers and storage already validated for Impact Level 5 workloads so the build can proceed through accreditation without redesign delays.
- Apply post-quantum encryption. Configure CNSA 2.0 cryptography for data at rest and in transit so the system stays protected against current and future decryption threats.
- Enforce CAC/PIV authentication. Integrate hardware-based identity verification so every user accessing the environment is authenticated through a credentialed smart card reader.
- Test and submit for authorization. Run classified content detection and security testing, then submit the completed package for CMMC or authority-to-operate review before going live.
Notably, skipping any one of these steps rarely saves time overall. Instead, it tends to resurface later during formal testing, which costs far more than addressing it upfront.
Air-Gapped AI vs Cloud-Based AI Gateways
Cloud-based AI gateways offer convenience, elastic scaling, and fast access to hundreds of models. However, they also route data through shared infrastructure that most classified programs simply cannot approve for use.
In contrast, disconnected AI environments trade some of that convenience for certainty. Nothing leaves the boundary, so there is no provider terms-of-service change, no silent model update, and no shared tenancy risk to monitor. Our analysis of why a provider's privacy policy is not a security strategy explains why this distinction matters even for unclassified but sensitive business data.
That said, a hybrid approach is often practical for organizations that need both flexibility and control. A gateway-first model — where sensitive workloads route to an air-gapped environment while lower-risk tasks use a governed cloud gateway — is explored in our piece on AI for regulated industries using a gateway-first approach.
Ultimately, the right choice depends on classification level, mission tempo, and budget. Agencies handling top secret or compartmented data rarely have a choice at all; isolation is mandatory.
Common Mistakes When Planning Air-Gapped AI Infrastructure
Even experienced program teams run into avoidable problems when designing an air-gapped AI deployment. Recognizing these patterns early can save months of rework.
First, many teams underestimate update logistics. Because the system has no internet connection, patches, model updates, and security signatures must be physically transferred in through an approved process, which takes planning that cloud-first teams rarely anticipate.
Second, skipping classified content detection is a frequent and costly oversight. Without automated scanning for sensitive terms and patterns, there is no safety net if a user accidentally feeds classified material into an unintended workflow. This gap also shows up in broader enterprise contexts; our guide on jailbreak detection for protecting enterprise AI covers related guardrail failures that apply even inside isolated environments.
Third, some teams assume a commercial cloud AI tool can simply be "moved" on-site. In reality, most consumer-facing AI products were never architected for isolation, which means the entire stack often needs to be rebuilt rather than relocated.
Frequently Asked Questions About Air-Gapped AI Deployments
What are air-gapped AI deployments?
Air-gapped AI deployments run AI models on hardware that is physically or logically isolated from the public internet and untrusted networks. This isolation prevents data exfiltration, external attacks, and unauthorized model access in classified or highly sensitive environments.
Why do government agencies need air-gapped AI instead of cloud AI?
Cloud AI platforms route data through shared infrastructure that most classified programs cannot approve for use. Air-gapped deployments keep inference and storage inside an accredited boundary, which satisfies IL5 and CMMC requirements that cloud-only tools cannot meet.
How long does it take to deploy an air-gapped AI system?
A straightforward single-site deployment can take two to six weeks once hardware and accreditation documentation are ready. SCIF-capable or multi-enclave rollouts with classified content detection typically take two to four months due to testing and authorization cycles.
What is the difference between air-gapped and on-premises AI?
On-premises AI simply means the hardware sits inside an organization's own facility, but it may still connect to the internet. Air-gapped AI goes further by removing or tightly controlling that external connection entirely.
Does CNSA 2.0 apply to air-gapped AI deployments?
Yes, CNSA 2.0 post-quantum cryptography standards increasingly apply to any system handling National Security Systems data, including air-gapped AI. Encrypting data at rest and in transit with CNSA 2.0 algorithms protects against future quantum decryption threats.
How much do air-gapped AI deployments cost compared to cloud AI?
Air-gapped deployments generally cost more upfront because they require dedicated hardware, accreditation support, and on-site maintenance. However, many agencies find the total cost justified by eliminating data breach exposure and recurring cloud compliance gaps.
What hardware is needed for an air-gapped AI deployment?
Typical hardware includes GPU-equipped servers, secure storage arrays, CAC/PIV-compatible authentication readers, and hardened network switches configured for isolation. SCIF-capable builds also require shielding and physical access controls.
Can air-gapped AI still use retrieval-augmented generation (RAG)?
Yes, retrieval-augmented generation, a method that lets AI pull facts from an internal knowledge base before answering, works fully offline. Indexing and vector search run entirely inside the isolated environment with no external calls.
What are common mistakes when planning air-gapped AI infrastructure?
Common mistakes include underestimating update and patching logistics, skipping classified content detection controls, and assuming commercial cloud tools can simply be relocated on-site. Each of these gaps can delay accreditation significantly.
Is CMMC Level 3 required for air-gapped AI deployments?
CMMC Level 3 alignment is required for defense contractors handling the most sensitive controlled unclassified information. Air-gapped AI deployments help satisfy many CMMC Level 3 controls by limiting network exposure and enforcing strict access management.
How do CAC and PIV cards fit into air-gapped AI security?
CAC and PIV cards provide hardware-based identity verification before a user can access an air-gapped AI system. This multi-factor control ensures only authorized, credentialed personnel reach classified AI workloads.
Can small defense contractors afford air-gapped AI deployments?
Smaller Defense Industrial Base contractors often adopt scaled-down air-gapped configurations rather than full SCIF builds. Tiered pricing and self-hosted options from vendors like AOCyber make entry-level compliant deployments more achievable.
Cross-functional review meetings help validate air-gapped AI deployments before formal authorization.
Bringing It All Together
Air-gapped AI deployments give defense, intelligence, and regulated enterprise teams a way to use modern AI without accepting the exposure that comes with public cloud connectivity. As outlined above, the strongest architectures combine strict boundary definition, post-quantum cryptography, CAC/PIV authentication, and classified content detection into a single accredited environment.
Consequently, organizations evaluating their next AI investment should treat isolation as a design requirement from day one rather than an afterthought bolted on before an audit. For teams exploring IL5-deployable, CMMC-aligned, and SCIF-capable AI infrastructure, AOCyber's government-grade AOCore platform is one option built specifically for this environment. In the end, a well-planned air-gapped AI deployment protects both the mission and the people who depend on it.