Role-based access AI systems are AI platforms that decide who can use which models, data, and tools based on a person's job role instead of their individual identity. As teams adopt chatbots, agents, and search over internal documents, this control becomes a basic safety layer. This guide explains how it works, how to set it up, and where teams go wrong.
Quick answer: Define roles by job function, give each role only the models, data, and actions it needs, tie roles to your identity system, and log every request. That is least privilege applied to AI.
A security team reviews permissions for role-based access AI systems.
What Is Role-Based Access Control for AI?
Role-based access control (RBAC) assigns permissions to roles, then assigns people to those roles. It is a long-established model, described by Wikipedia's RBAC overview and supported by NIST standards work. In AI, the same idea applies to new kinds of resources.
Those resources include language models, document collections, web search, image generation, and API keys. A finance analyst may need a private knowledge base of reports. A developer may need several models through one API. Neither needs the other's access.
Why AI Needs Stricter Access Than Typical Software
AI tools differ from ordinary apps in three ways. First, they ingest free-form text, so users may paste sensitive data without thinking. Second, they can retrieve content from many sources at once. Third, agents can take actions, not just answer questions.
As a result, one over-permissioned account can expose far more than before. Unmanaged tools make this worse, as explained in our look at shadow AI in the enterprise.
What an AI Role Should Control
Model and Tool Access
Decide which models each role may call. Some teams restrict powerful or costly models to specific groups. Likewise, limit tools such as web search, code execution, or file export.
Data and Knowledge-Base Access
Retrieval-augmented generation (RAG) lets an AI answer from your documents. Retrieval must honor document permissions. Otherwise, the AI becomes a way around your existing controls.
Budgets and Guardrails
Roles can also carry usage caps and content rules. For example, a support role might have stricter content filters than a security research role. Our piece on content guardrails for agentic AI covers this in more depth.
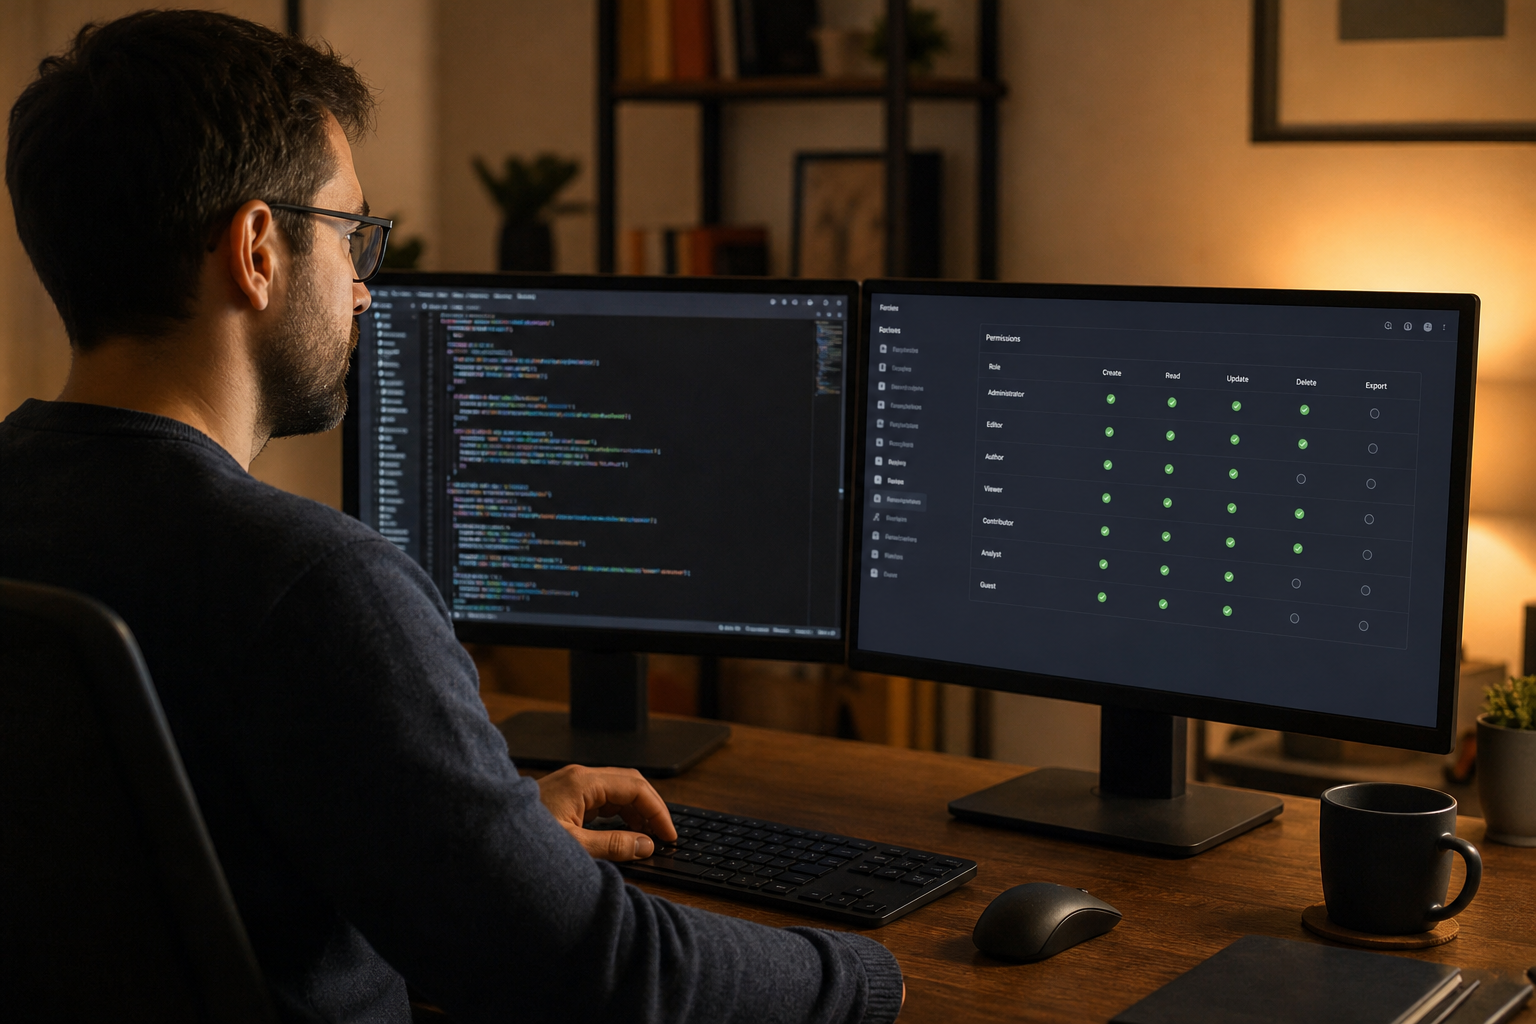
Developers often need broader model access than other roles, but not broader data access.
How to Implement Role-Based Access in AI Deployments
Follow these steps to build a workable policy.
- Inventory AI assets. List every model, knowledge base, tool, and integration, and note how sensitive each is.
- Define roles. Base them on job function, such as analyst, developer, or administrator.
- Map permissions. Grant the minimum each role needs and deny everything else by default.
- Connect identity. Link roles to your identity provider so group membership drives access.
- Log and review. Record each request by user, role, and model, and remove unused permissions on a schedule.
Role-Based Access Combined with Data Protection
RBAC decides who gets in. It does not inspect what they send. Therefore, pair it with controls such as PII tokenization, which replaces personal data with placeholders before it reaches a model. Prompt-injection detection adds another layer.
Moreover, a central gateway makes this easier. With one entry point, you enforce roles, budgets, and logging in one place instead of in every app.
Access Control for Government and Regulated Teams
Defense and regulated organizations face stricter rules. Identity often rests on hardware credentials such as CAC or PIV cards. For details, see how CAC/PIV integration secures government AI access.
In these settings, classification levels also shape roles. A user cleared for one level should never reach content above it through an AI shortcut.
Common Mistakes to Avoid
- Sharing one API key across a whole team.
- Creating a single "admin" role that too many people hold.
- Tying permissions to named people instead of functions.
- Skipping audit logs, which leaves no evidence after an incident.
- Letting AI agents inherit a human's full permissions.
Where aocyber.ai Fits
aocyber.ai builds privacy-first AI software. Its AOCore gateway offers one OpenAI-compatible API to 500+ models, with AOSentry providing PII tokenization, content guardrails, and jailbreak detection. AODex is a private AI workspace with persistent memory and knowledge-base search, and it runs on AI hosted by AOCyber. Teams can also use tuned personas for specific domains. Evaluate any vendor on the criteria above: role granularity, identity integration, logging, and data ownership.
Frequently Asked Questions
What are role-based access AI systems?
Role-based access AI systems are AI platforms that grant permissions by role instead of by individual. Each role defines which models, data, and actions a user may use.
Why does AI need role-based access control?
AI tools can read sensitive data and take actions on a user's behalf. Role-based controls limit exposure if an account is misused or an AI output goes wrong.
How is RBAC different from attribute-based access control?
RBAC decides access from a user's role. Attribute-based control (ABAC) uses attributes such as location, device, or data classification. Many organizations combine both.
What should an AI access policy cover?
It should cover model access, knowledge-base access, tool and API permissions, spending limits, and logging. It should also name who approves changes.
Can RBAC stop prompt injection?
Not by itself. RBAC limits the damage an injected prompt can cause, but you still need guardrails and detection to catch the attack.
How do I apply least privilege to AI agents?
Give each agent its own identity and only the tools and data its task requires. Avoid sharing one broad service account across agents.
How often should AI roles be reviewed?
Review them at least quarterly and whenever someone changes jobs. Regular reviews catch permission creep before it becomes a risk.
What are common RBAC mistakes in AI deployments?
Common mistakes include shared API keys, overly broad admin roles, roles tied to people instead of functions, and missing audit logs.
Does RBAC apply to knowledge-base search?
Yes. Retrieval should respect the same permissions as the source documents, so users only get answers drawn from content they may see.
How does RBAC help with compliance?
It gives auditors clear evidence of who can access what. Frameworks such as NIST SP 800-53 include access control and audit requirements.
How long does it take to set up RBAC for AI?
A small team can define core roles in a day or two. Larger organizations need more time to map data and integrate identity systems.
Can budget limits be part of role-based access?
Yes. Many AI gateways let you set spending or usage caps per role or team, which prevents runaway costs.
Conclusion
Strong role-based access AI systems start with a clear inventory, function-based roles, least-privilege permissions, identity integration, and regular review. Pair them with data protection and logging, and AI adoption becomes far safer to scale. To see how a private, governed AI stack can support this, visit aocyber.ai.

